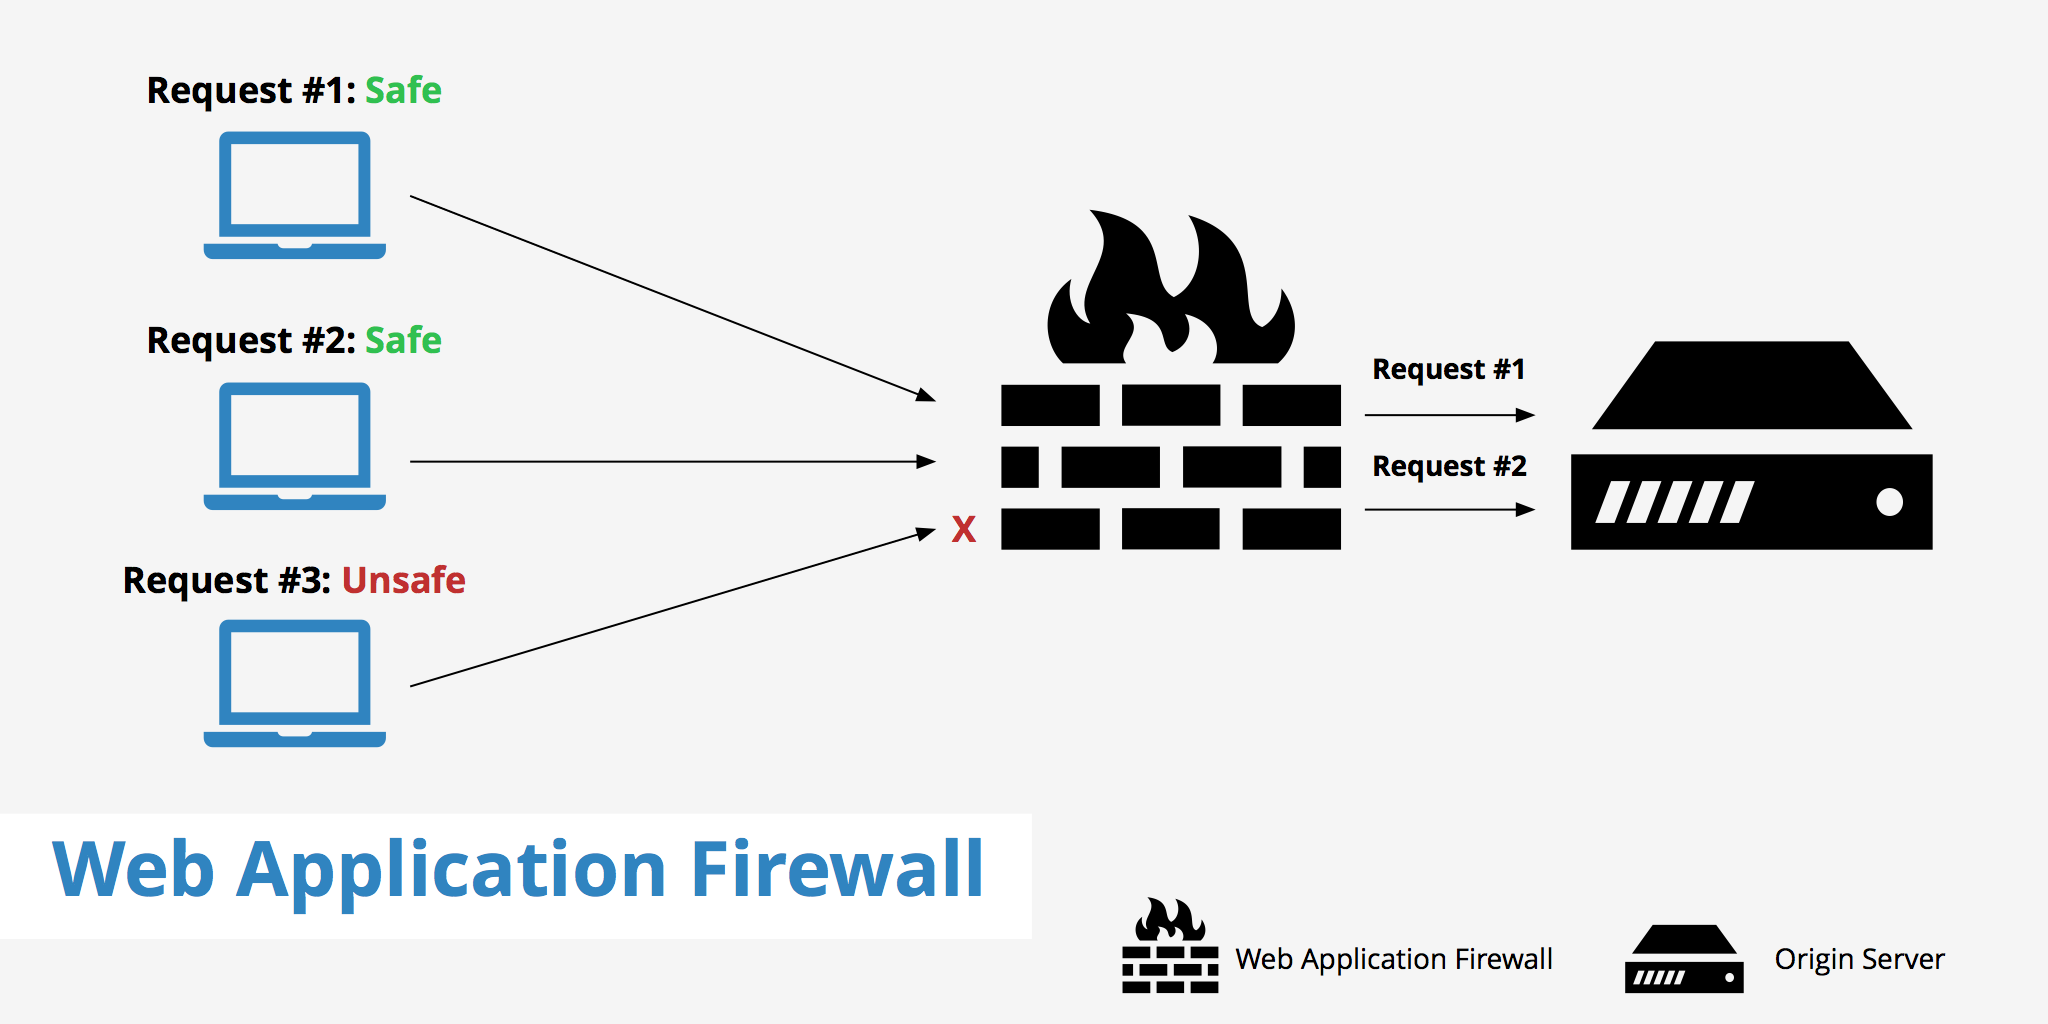
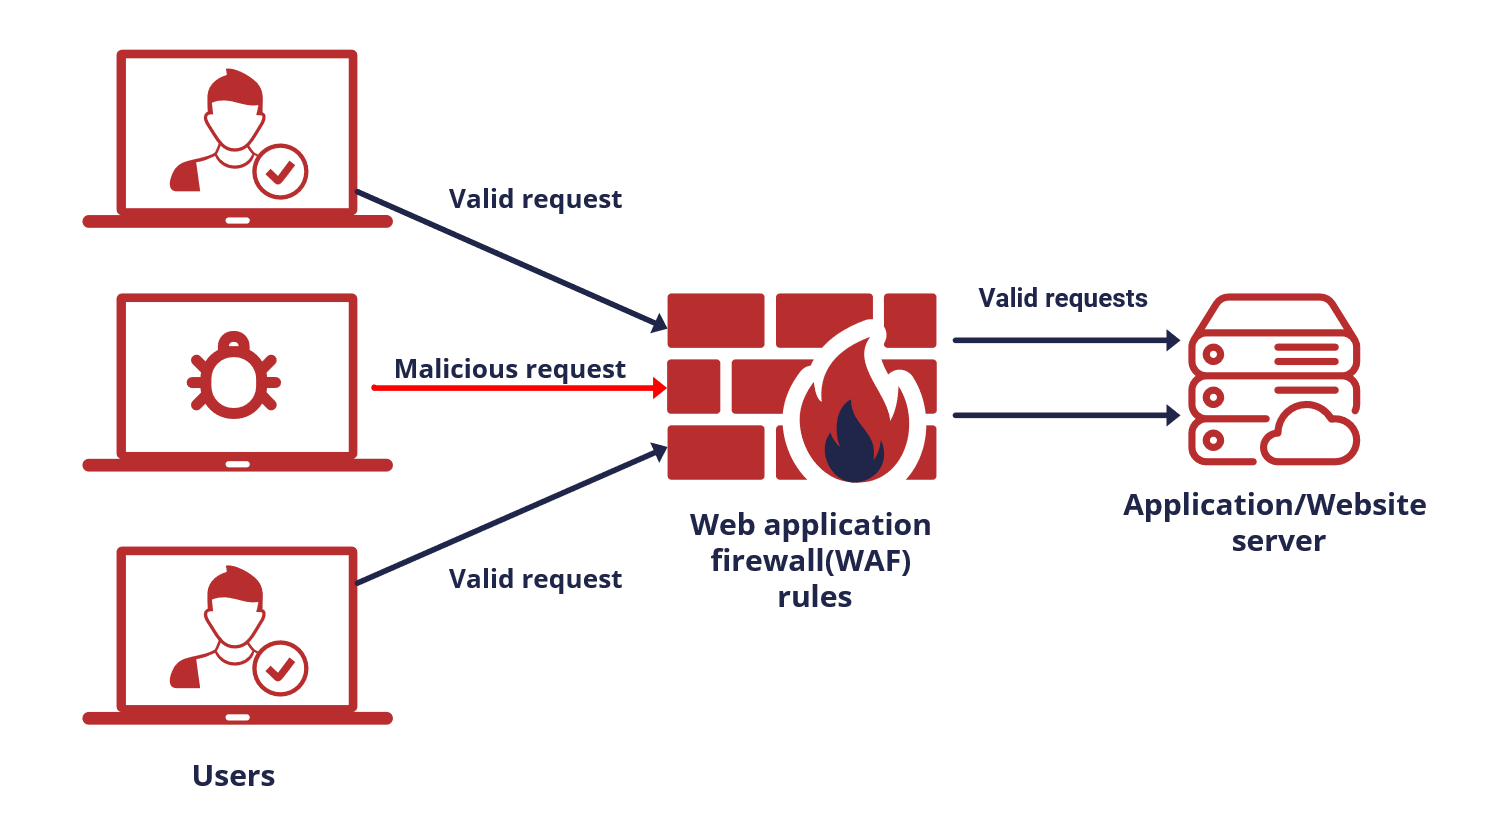
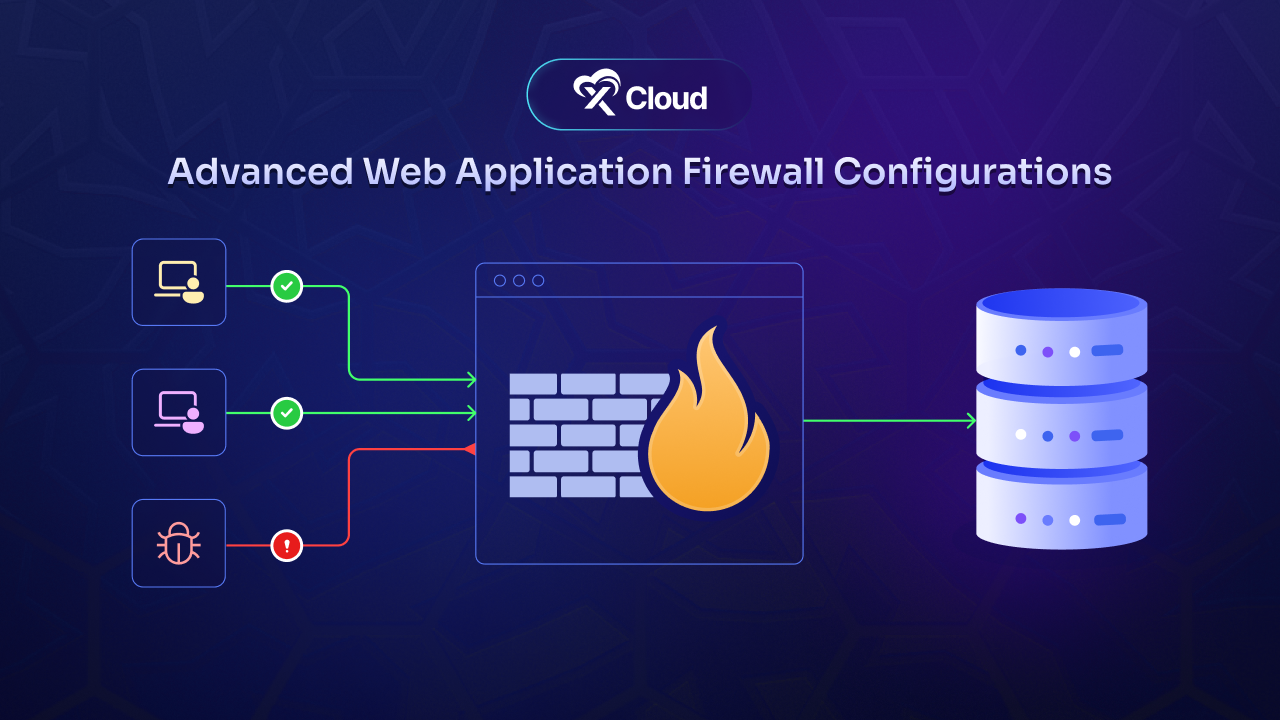
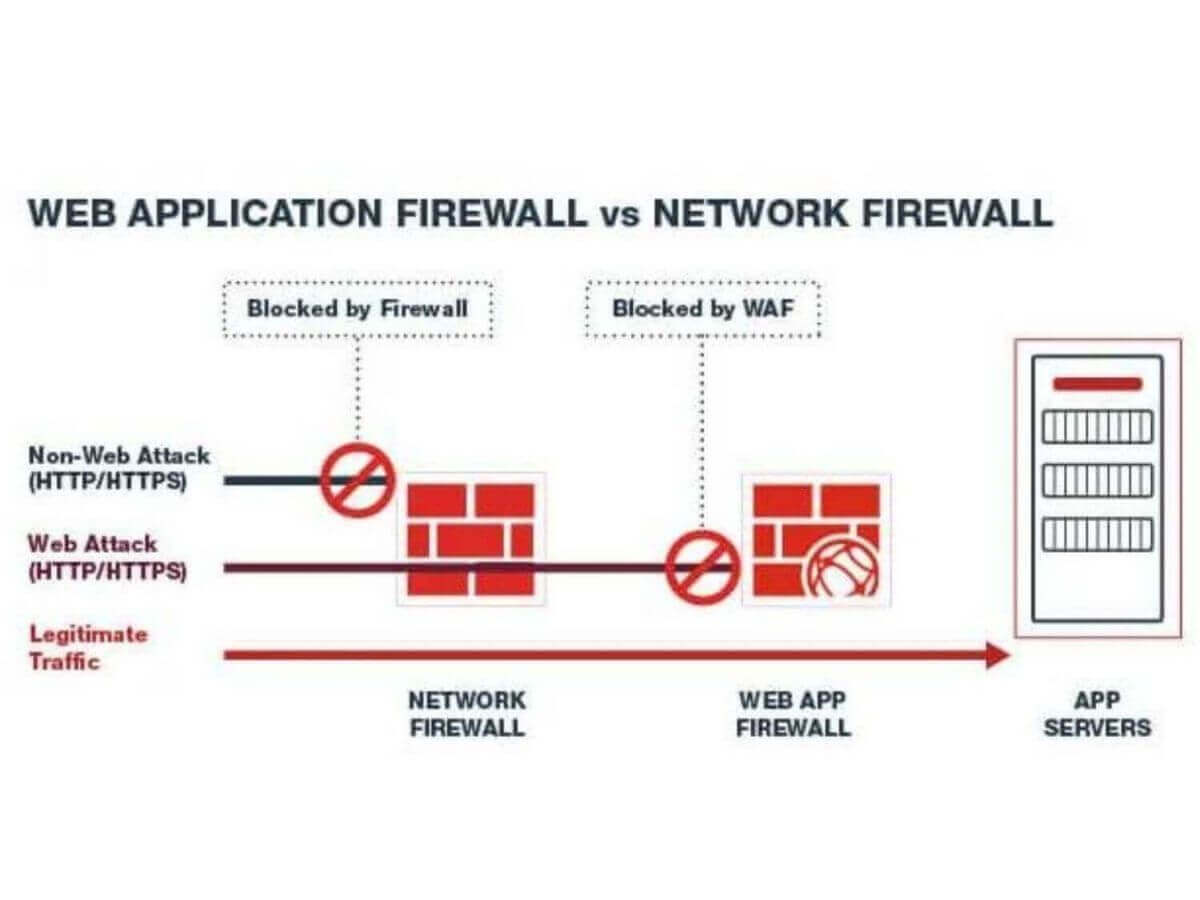
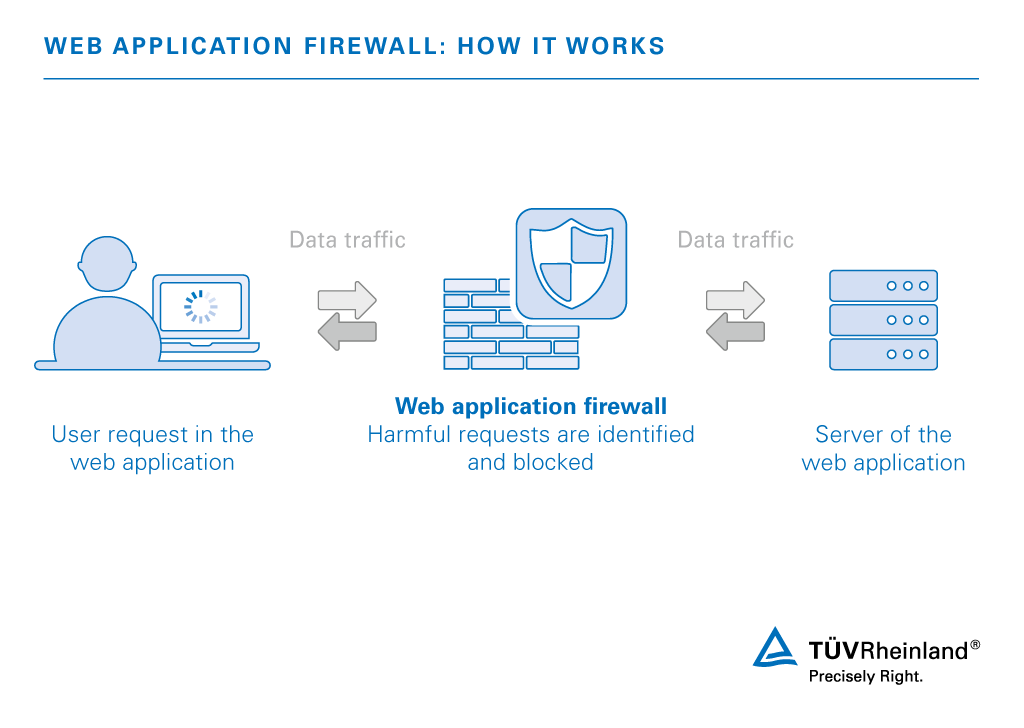
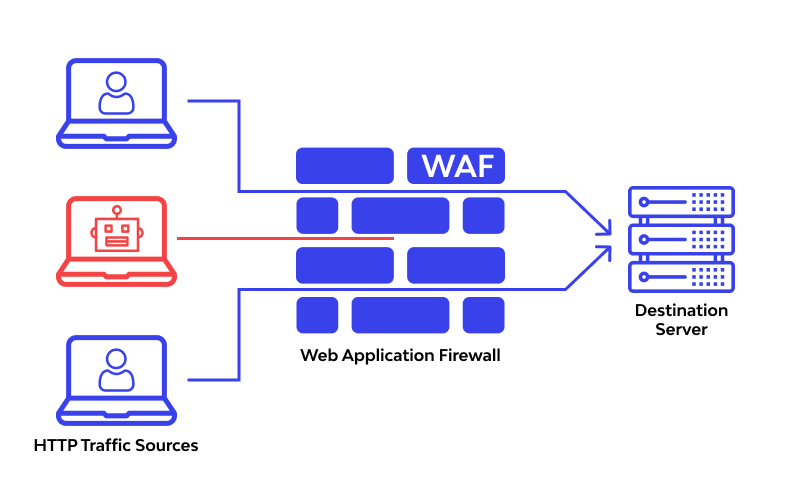
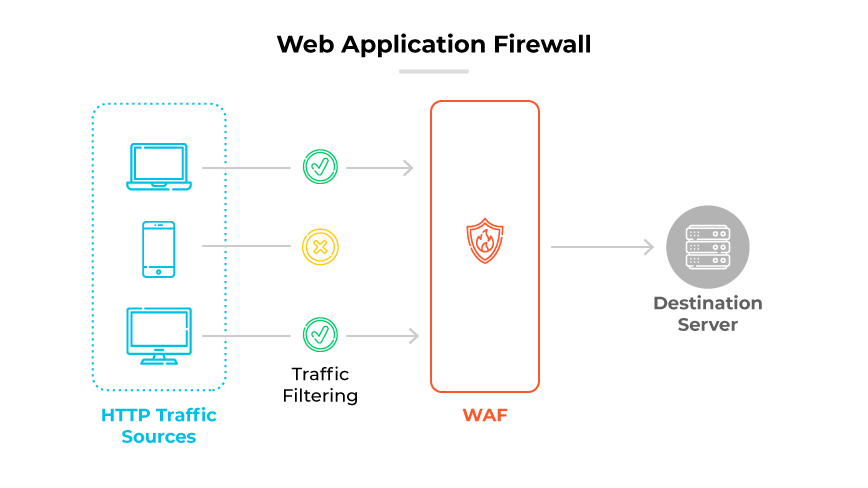
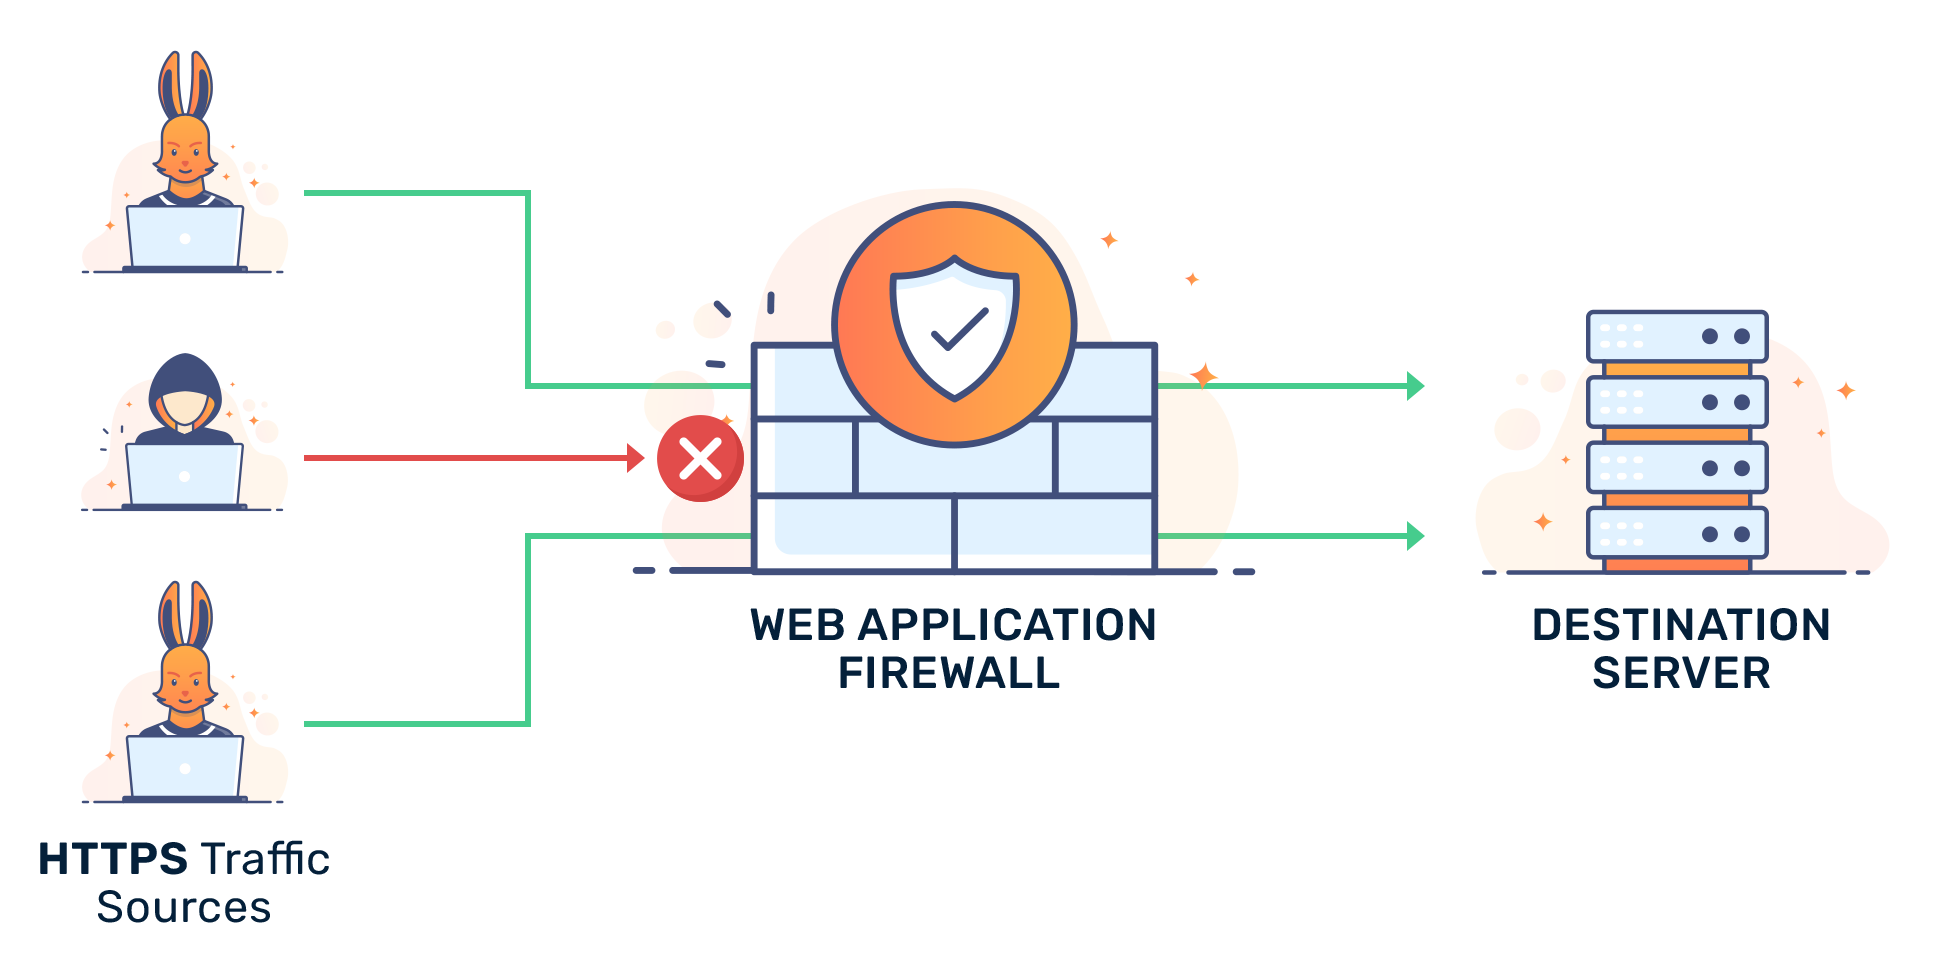
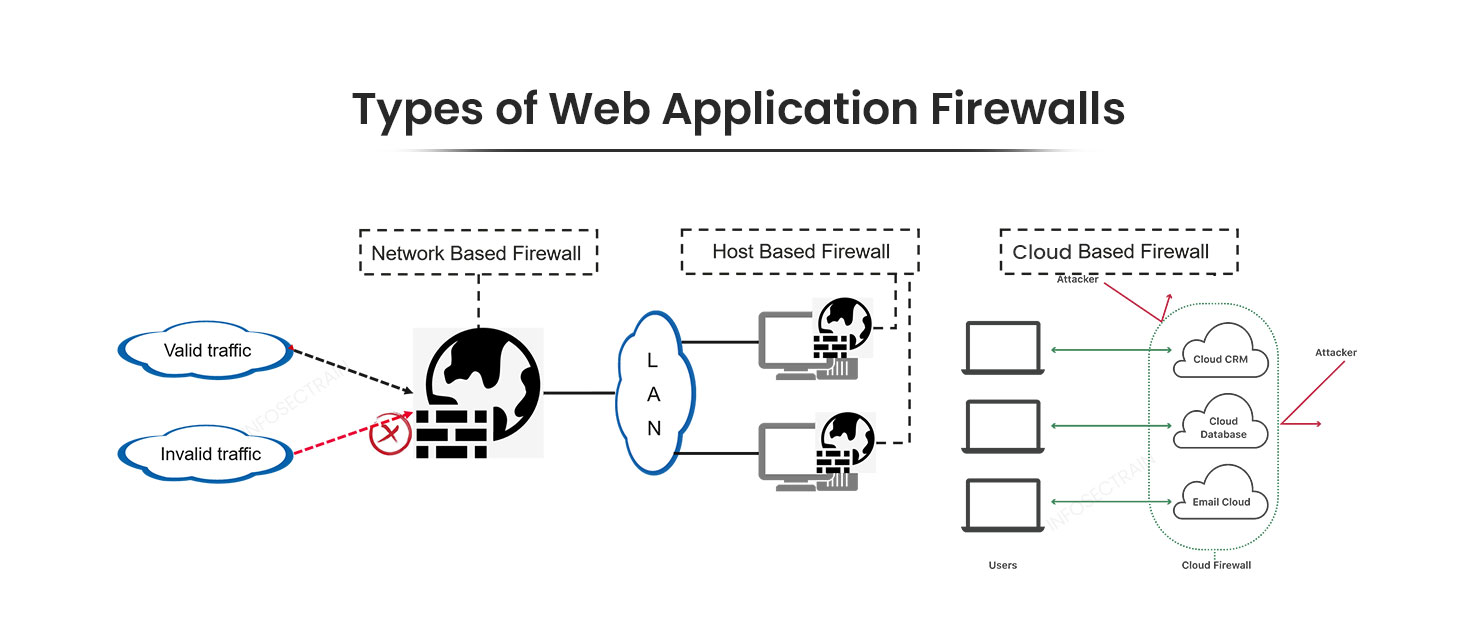
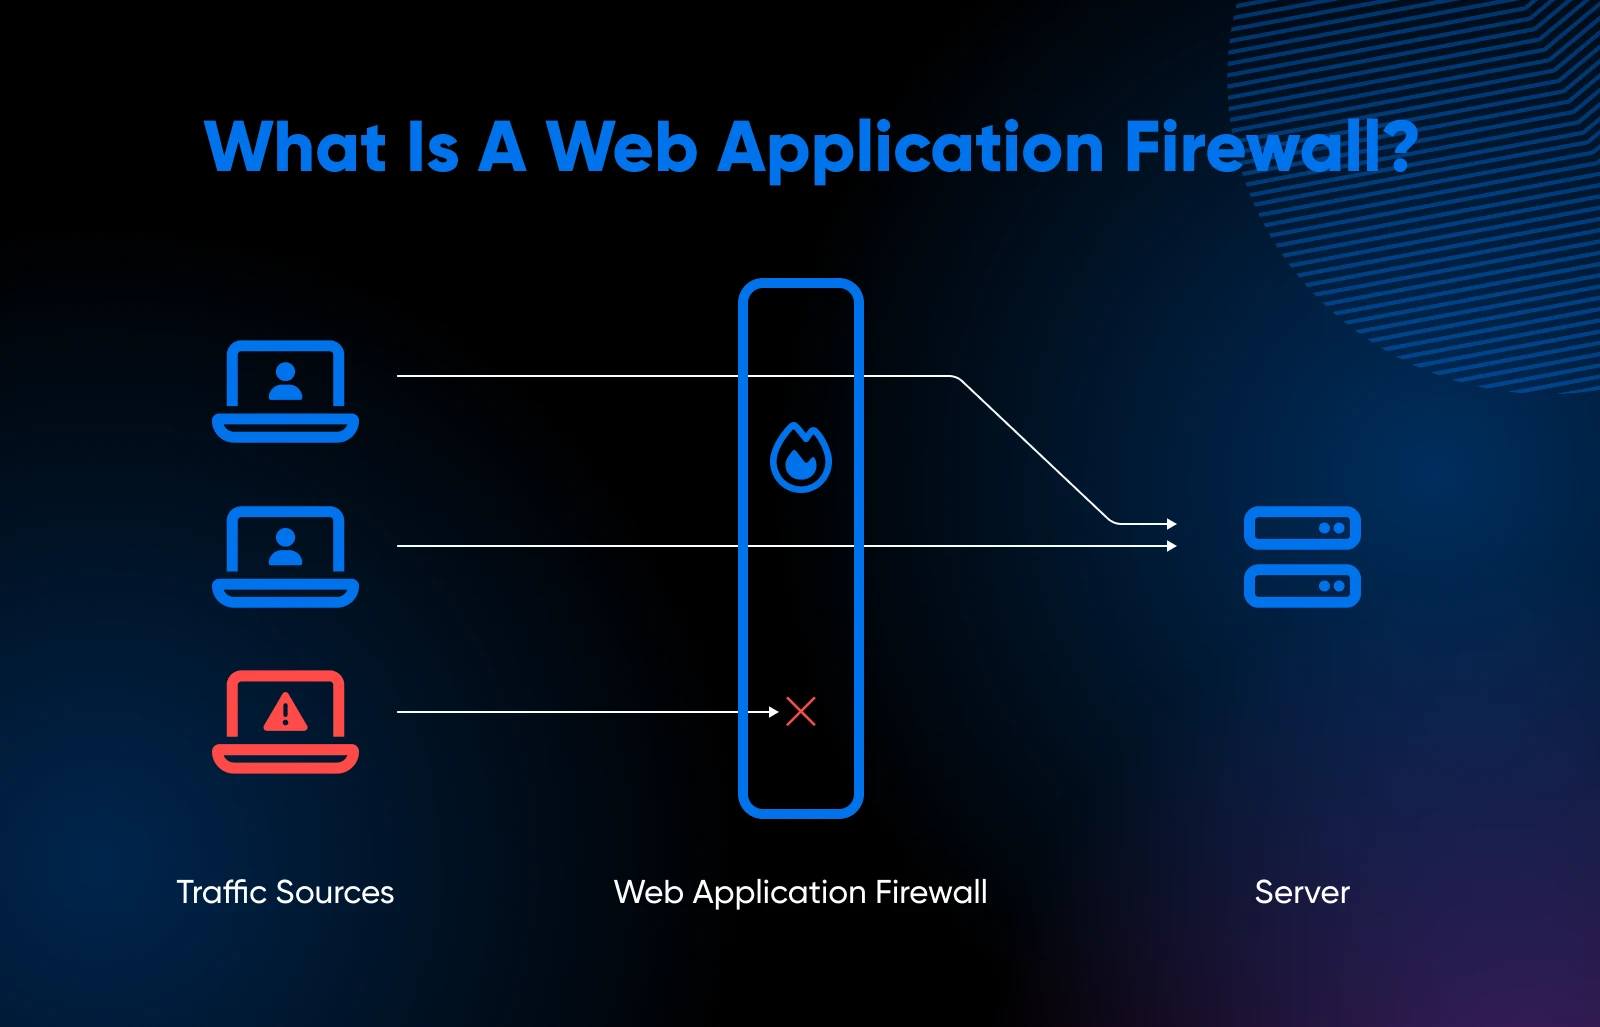
A Web application firewall (WAF) is a specific form of application firewall that filters, monitors, and blocks HTTP traffic to and from a web service. By inspecting HTTP traffic, it can prevent attacks exploiting a Web application's known vulnerabilities, such as SQL injection, cross-site scripting (XSS), file inclusion, and improper system configuration. Financial institutions often utilize WAFs to help in the mitigation of Web application zero-day vulnerabilities, as well as hard-to-patch bugs or weaknesses through custom attack signature strings.
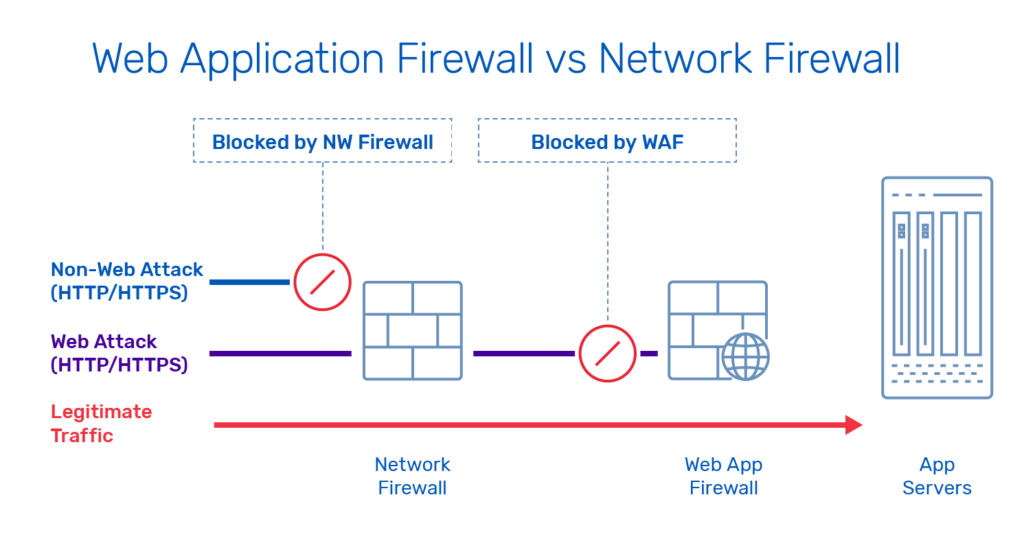
Web Application Firewall (WAF) provides centralized protection of your web applications from common exploits and vulnerabilities. Web applications are increasingly targeted by malicious attacks that exploit commonly known vulnerabilities. SQL injection and cross-site scripting are among the most common attacks. Preventing such attacks in application code is challenging. It can require rigorous maintenance, patching, and monitoring at multiple layers of the application topology. A centralized web application firewall helps make security management much simpler. A WAF also gives application administrators better assurance of protection against threats and intrusions. See full list on learn.microsoft.com WAF can be deployed with Azure Application Gateway, Azure Front Door, and Azure Content Delivery Network (CDN) service from Microsoft. WAF on Azure CDN is currently under public preview. WAF has features that are customized for each specific service. For more information about WAF features for each service, see the overview for each service. See full list on learn.microsoft.com For more information about Web Application Firewall on Application Gateway, see Web Application Firewall on Azure Application Gateway. For more information about Web Application Firewall on Azure Front Door Service, see Web Application Firewall on Azure Front Door Service. For more information about Web Application Firewall on Azure CDN Service, see Web Application Firewall on Azure CDN Service To learn more about Web Application Firewall, see Learn module: Introduction to Azure Web Application Firewall. See full list on learn.microsoft.com A web application firewall or WAF is a security tool that protects web applications against common web-based threats by monitoring, filtering, and blocking data packets. A Web application firewall (WAF) is a specific form of application firewall that filters, monitors, and blocks HTTP traffic to and from a web service. By inspecting HTTP traffic, it can prevent attacks exploiting a Web application's known vulnerabilities, such as SQL injection, cross-site scripting (XSS), file inclusion, and improper system ... A web application firewall (WAF) is a security solution that protects web applications from common attacks, such as SQL injection, cross-site scripting (XSS), and distributed denial-of-service (DDoS). WAFs monitor and filter HTTP/HTTPS traffic between clients and web applications, enabling organizations to implement custom security rules and block malicious requests. In contrast, an ... Policy in Web Application Firewall: The set of rules through which a WAF operates is called a policy. The purpose of these policies is to protect against the vulnerabilities in the application by filtering out malicious traffic. The value of a WAF comes in part depending upon the speed and efficiency with which the policy modification is ... What is a web attack mitigation (WAF)? This method of attack mitigation is usually part of a suite of tools which together create a holistic defense against a range of attack vectors. By deploying a WAF in front of a web application, a shield is placed between the web application and the Internet. What is a web application firewall? Since web and mobile applications and APIs are prone to security risks that can disrupt operations or exhaust resources, web application firewalls are designed to counter common web exploits like malicious bots. WAFs safeguard against threats that compromise availability, security, or resources including zero-day exploits, bots, and malware. What is a web application firewall (WAF)? A WAF or web application firewall helps protect web applications by filtering and monitoring HTTP traffic between a web application and the Internet. It typically protects web applications from attacks such as cross-site forgery, cross-site-scripting (XSS), file inclusion, and SQL injection, among others. What is Azure web application firewall? Azure Web Application Firewall is one of the services in the category of network security for Azure. Other services in this category include Azure DDoS Protection and Azure Firewall. Each service has its own unique features and use cases. For more information on this service category, see What is Azure network security? Understanding what is a web application firewall starts with recognizing that network firewalls and intrusion-prevention systems work at lower network layers. WAF security operates at the application layer to stop business-logic abuse and feed clean, high-fidelity events into your security stack.

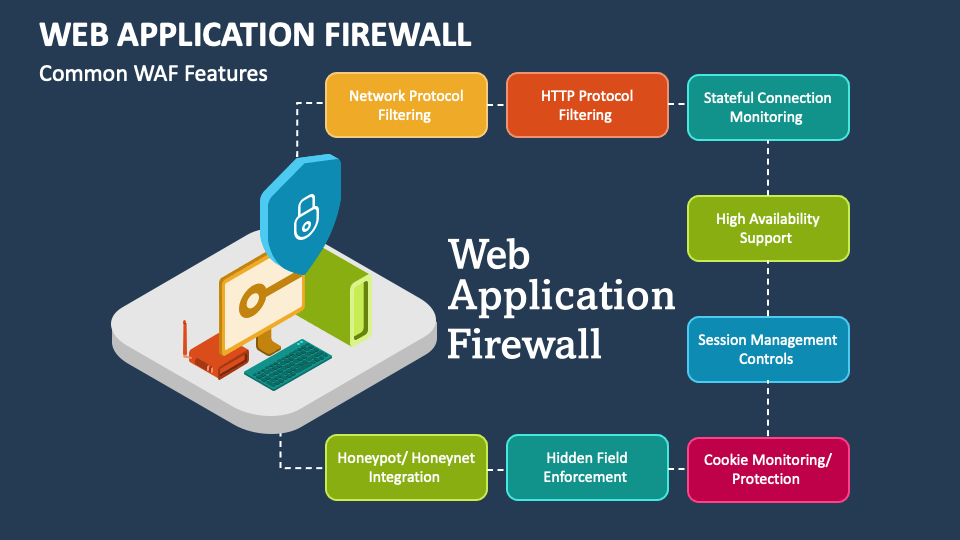
As we can see from the illustration, Web Application Firewall has many fascinating aspects to explore.
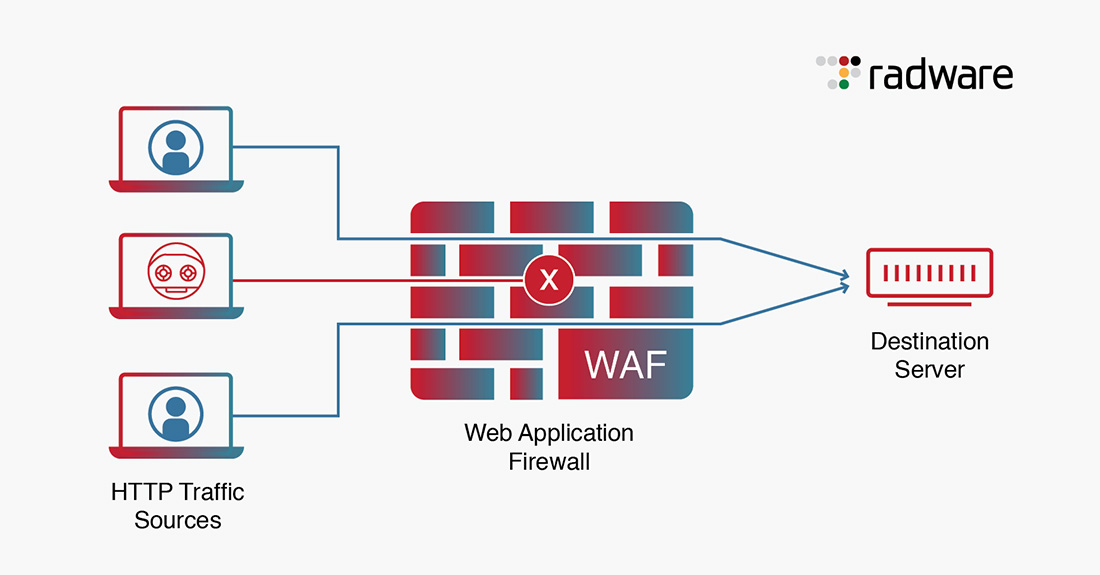
As we can see from the illustration, Web Application Firewall has many fascinating aspects to explore.